

Compliance · Cyber risk · Audit
Risk & Compliance Management Platform
Bring policy, cyber risk, incident response and audit evidence into one platform. Know where you stand, and prove it to any regulator, board, insurer or client, without rebuilding the record before every audit.
- ISO 27001-certified team (view certificate, opens in a new tab)
- Set up and supported by Knowall
- Supporting UK businesses since 1999
Request a callback
A no-obligation chat about the platform. Leave your details and our team will call you back.
Prefer to talk now? Call 020 7471 3270
The gaps that leave businesses exposed
- 31% have board-level responsibility for cyber security
- 25% have a formal incident response plan
- 15% review the cyber risks posed by their suppliers
UK businesses. Source: Cyber Security Breaches Survey 2025/26, UK Government (DSIT).
Most businesses manage compliance in spreadsheets, shared folders and inboxes. It works until an auditor, insurer or client asks for proof.
Why our platform pays off
-
One platform, not ten tools
Policy, compliance, risk, incidents and audit in a single system instead of spreadsheets and separate dashboards.
-
Audit-ready every day
Evidence is captured as the work happens, so audit packs are built from what already happened.
-
Know your exposure
Model your cyber risk exposure and the impact of an incident, and share evidence with insurers and brokers.
-
Incidents with proof
Every action, decision and timeline captured live for regulators, clients and insurers.
-
Spot risk early
Ongoing monitoring of assets, suppliers and configurations flags problems as they appear, not at your next review.
-
Backed by people
Set up, run and supported by our ISO 27001-certified London team.
What the platform does
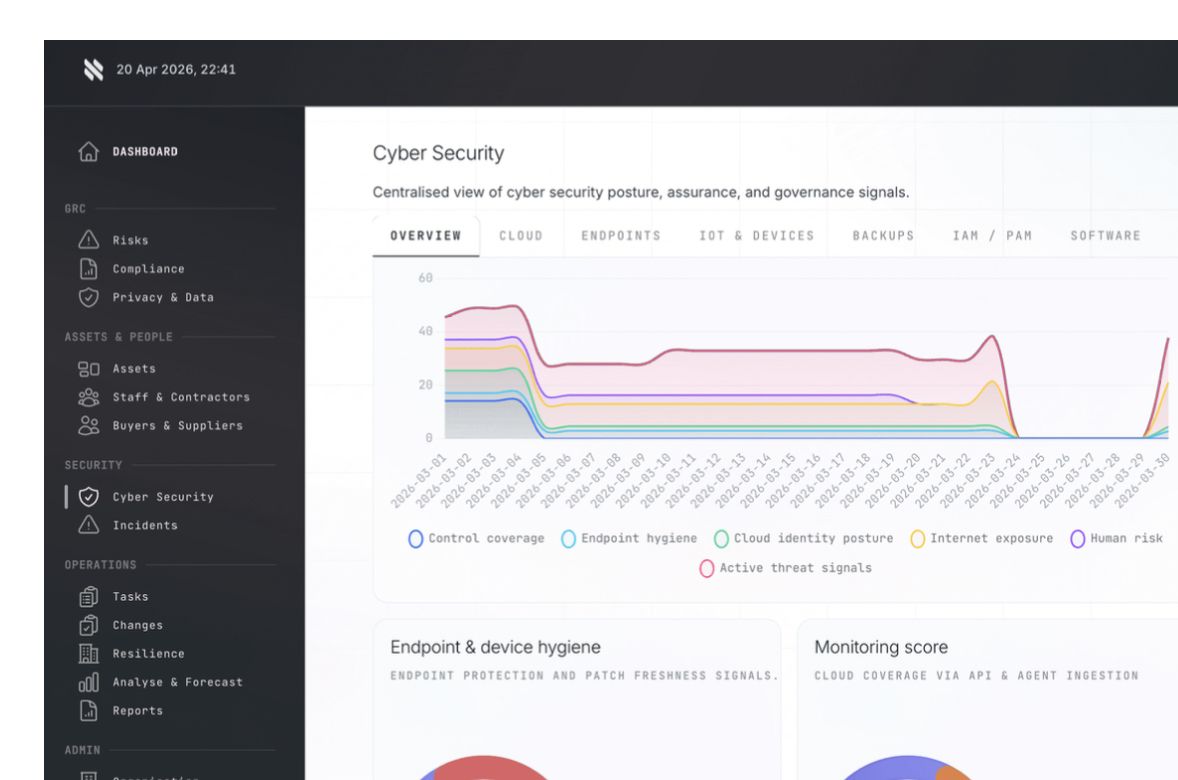
Fix what attackers can actually exploit
Focus on the vulnerabilities that matter and track each one to closure, with evidence attached.
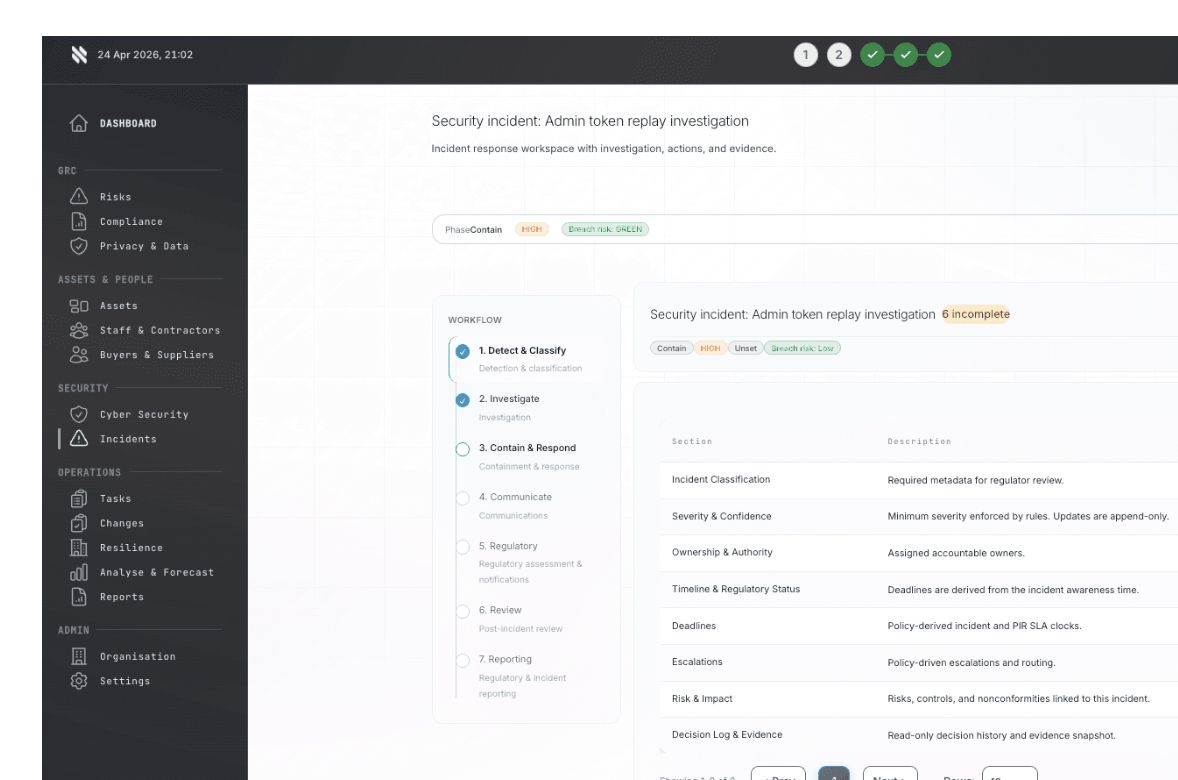
Run incidents in one place
Clocks, escalations and notifications, with proof captured as it happens.
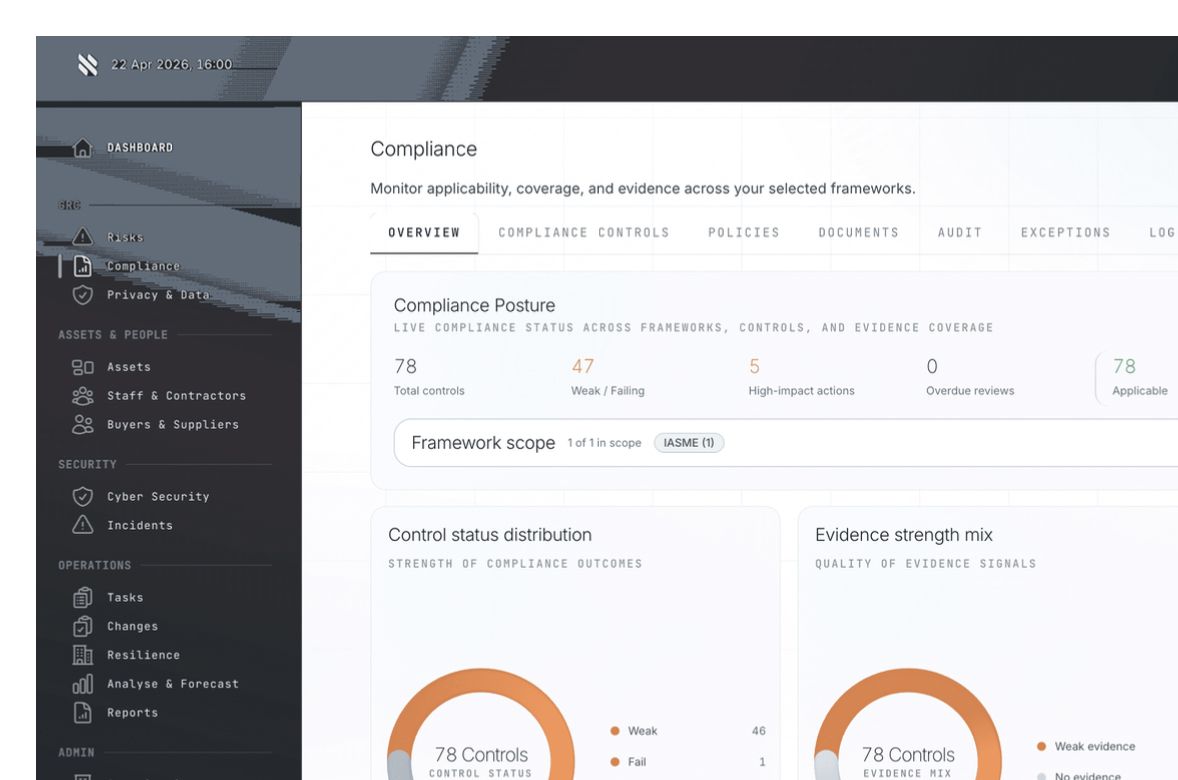
Map controls once
Collect evidence continuously and reuse it across every framework you answer to.
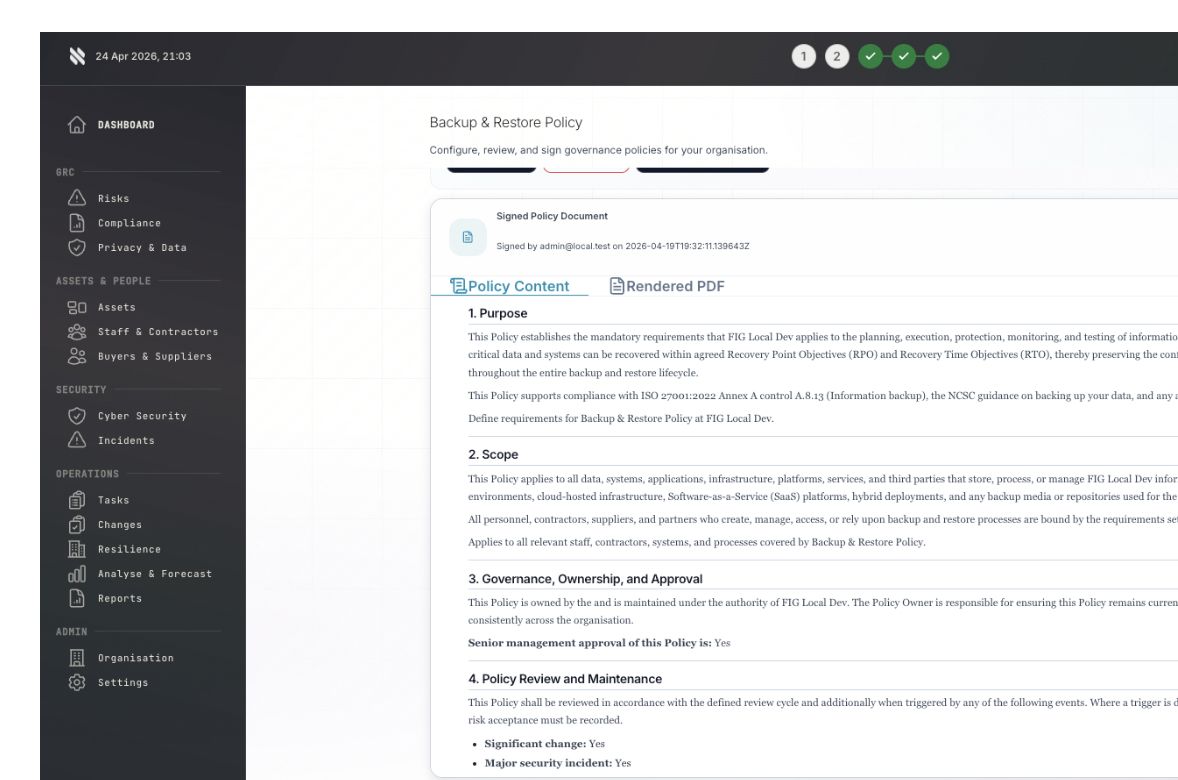
Make policies work
Manage policies from drafting through approval to staff sign-off, with workflows, owners and a record of every action.
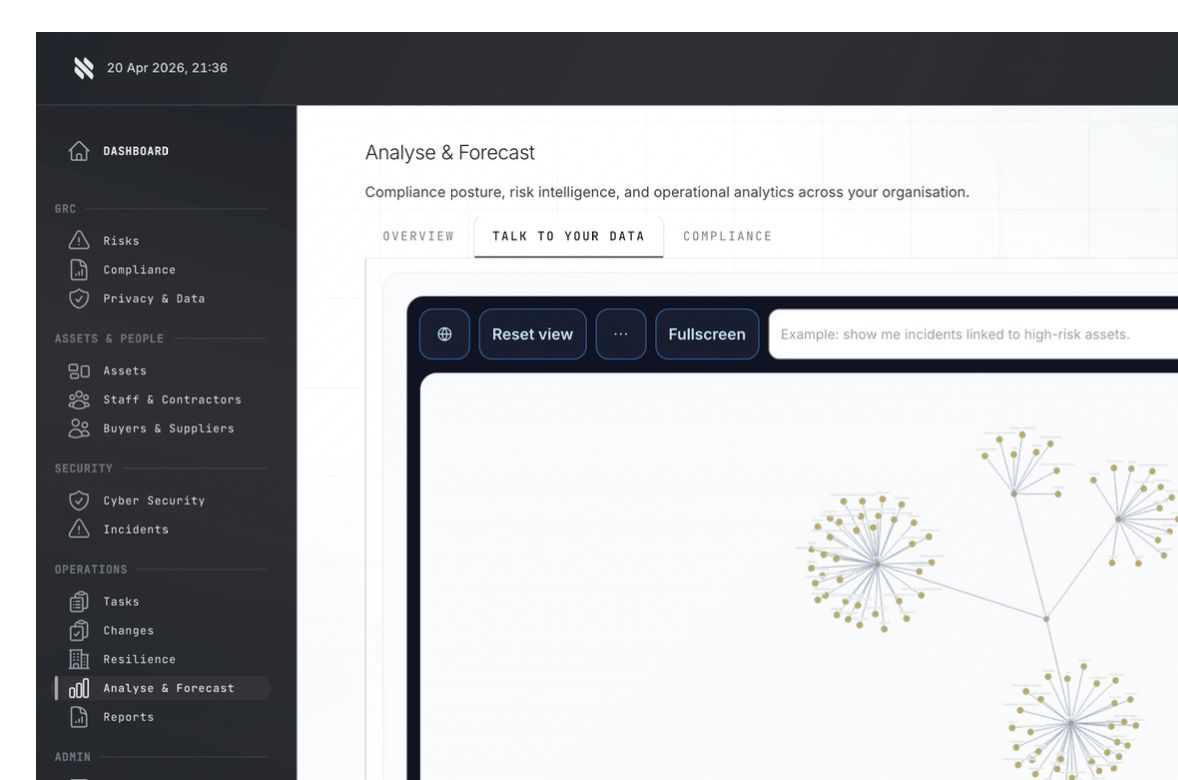
Find and protect sensitive data
Locate, classify and monitor sensitive data across devices, cloud and storage.
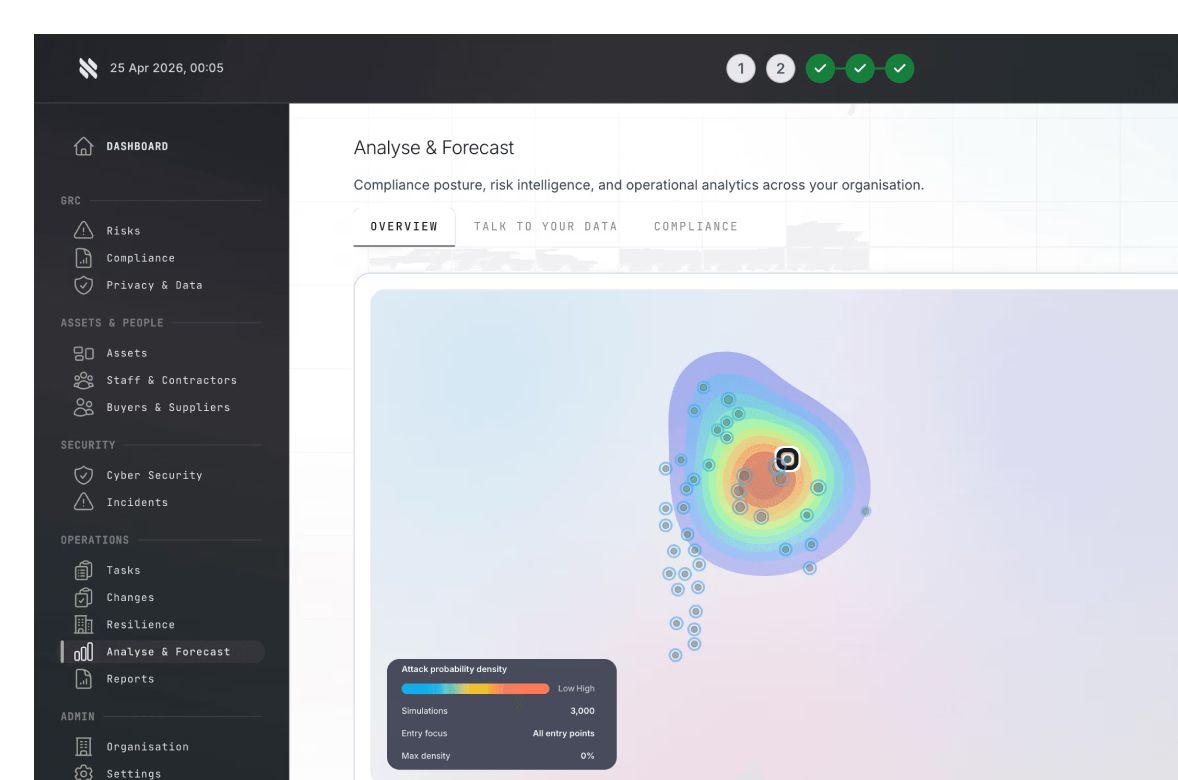
See your cyber exposure
Model your aggregate risk exposure and what an incident could cost, so you see it before a breach, not during one.
-
Manage supplier risk
Ongoing monitoring of third parties, with control assessments and risk scores.
-
Train and track your staff
Assign compliance training and policy sign-offs, and keep the evidence.
Built around the standards you answer to
Map your controls once and reuse the evidence across 65+ frameworks, including:
- ISO 27001
- Cyber Essentials
- UK GDPR
- NIST CSF
- PCI DSS
- SOC 2
- FCA obligations
- NHS DSPT
- NIS2
Working towards certification?
The platform ties in with our Cyber Essentials and Cyber Essentials Plus service.
Who it’s for
For businesses that answer to regulators, insurers, boards or demanding clients: law firms, financial services, accountancy practices and any organisation that has to prove its security, not just claim it.
-
Law firms
Answer client security questionnaires and panel requirements with evidence, not promises. Keep GDPR, Cyber Essentials and ISO 27001 controls in one place.
-
Financial services
Map controls to FCA obligations, PCI DSS and SOC 2, and keep an auditable record of incidents and decisions for regulators.
-
Accountancy practices
Protect client financial data, track GDPR obligations and show insurers and clients exactly where you stand.
-
Businesses in supply chains and tenders
Larger clients and public-sector buyers increasingly ask suppliers to prove their security. Keep certificates, policies and evidence ready to share.
See the platform in action
Book a short walkthrough and we’ll map the platform against the frameworks and risks that matter to your business.
The platform and the people behind it
Software alone doesn’t make you compliant. Our ISO 27001-certified London team sets the platform up, configures it around your frameworks and supports you day to day, so the people closest to the work can run it without a dedicated compliance team. We’ve managed IT and cyber security for London businesses since 1999.
Want to see where your compliance and exposure sit today? Book a short walkthrough.
Risk & compliance platform FAQs
-
What is the Compliance Platform?
It’s a single governed system that brings your policies, cyber risk, incident response and audit evidence into one place. Instead of juggling spreadsheets and disconnected tools, you manage compliance as one continuous workflow, so you know where you stand and can prove it on demand.
-
Which frameworks and standards does it support?
The platform supports 65+ frameworks, including ISO 27001, Cyber Essentials, UK GDPR, NIST CSF, PCI DSS, SOC 2 and FCA obligations. It maps your controls to several at once, so you collect evidence once and reuse it. Tell us which standards apply and we’ll recommend the right package.
-
How is this different from a spreadsheet or a standard GRC tool?
Most tools record what already happened. This one drives what happens next: controls generate tasks with assigned owners, remediation runs through approval workflows, and every action is recorded. Compliance becomes a continuous part of how you work, not a quarterly project.
-
What actually happens when we have a cyber incident?
You run the whole response inside the platform, with clocks, escalation paths, regulatory notifications and reviews built in. Every action, decision and timeline is captured as the work happens, so when a regulator, client or insurer asks, you have a defensible record ready rather than reconstructing it after the fact.
-
Does it really keep us audit-ready all the time?
Yes. Because evidence is captured as work happens, your audit packs are built from what already took place. There’s no last-minute scramble to assemble proof before a deadline. The record is always current.
-
Do we need a dedicated compliance team to run it?
No. It’s designed to be operated by the people closest to the work, with our ISO 27001-certified London team handling setup, configuration and ongoing support. You get the platform and the people behind it.
-
How does exposure modelling work?
The platform models your aggregate risk exposure and the likely impact of incident scenarios, based on your assets, security findings and suppliers. You can also build evidence packs to share with insurers, brokers or underwriters.
-
How long does it take to get started?
Initial set-up can be live in as little as 48 hours. Full roll-out depends on the size of your estate and the frameworks in scope. The fastest way to get a realistic timeline is a short walkthrough, where we map the platform against your environment and show you where your compliance and exposure sit today.
-
How much does the platform cost?
Pricing depends on your organisation’s size and the frameworks you need. Book a walkthrough and we’ll recommend a package and send a clear quote.
-
Is our data secure?
Yes. The platform is built for security and compliance governance, with access controls and a full record of activity. Our ISO 27001-certified team handles your set-up and day-to-day support.
Know where you stand, and prove it
Book a short walkthrough with our team.